Home / Change requested vs what ran
They requested ABC. They did DEF.
Change requested versus what ran is the gap between what a change record approved and what the pipeline and runtime actually did. Quantlyx shows every place the two disagree while the identity is still in use, with the evidence attached, so the practitioner can still act.
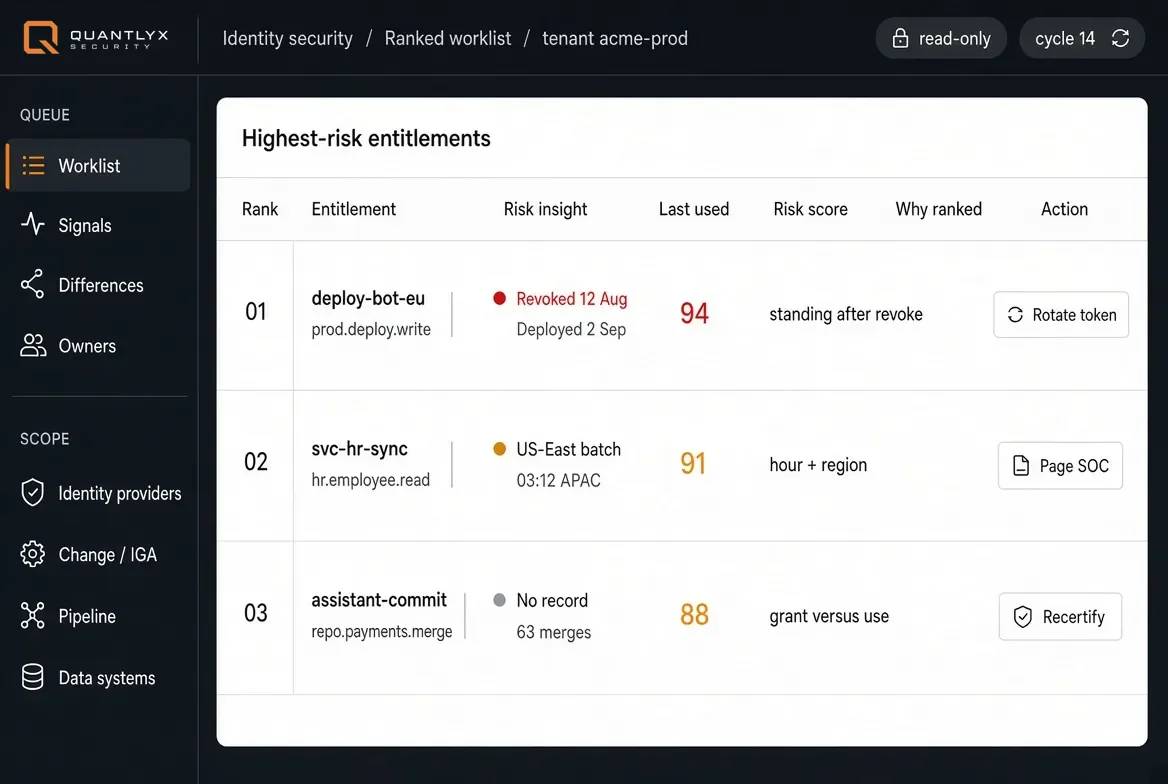
Each difference carries the evidence that produced it.
Two records that should agree
What was requested
The change record, the ticket and the entitlement approval: the action a person approved, under what authority, for how long.
What ran
What was committed, built, deployed and run, by which identity, with the commit, build, deployment or checkout that produced it.
The gap, early
Every disagreement becomes a line on a ranked worklist with the evidence attached, while the identity can still be stopped.
What the disagreement looks like
Approved for a person, made by a bot
The change was approved for a human. The pipeline shows an automation identity made it.
Pipeline identities nobody enrolled
Identities that build and deploy with no owner and no record of who approved them.
Revoked in the record, still deploying
The entitlement was revoked in the governance record while the token behind it still deploys.
Break-glass used as the normal release
Emergency access used for routine releases, with no incident behind it.
From the gap to the action
Each difference is scored as a SOC-ready signal in the NHI misuse threat library and routed to the SIEM, the service desk and change management. The accountable owner gets the evidence, and QuantQFix proposes the fix for a person to approve. Quantlyx never blocks a build, a merge or a release.
See NHI misuse on your tenant
Read-only pilot. One lifecycle path. If nothing turns up, you keep a clean report.