Home / Solutions / Security leaders
Identity security platform for CISOs
Quantlyx is an identity security platform that gives a chief information security officer a ranked list of entitlement risk across people, service accounts, build identities, release bots and coding agents. Every line carries the evidence and a named owner, so the risk you take upstairs is one you can defend.
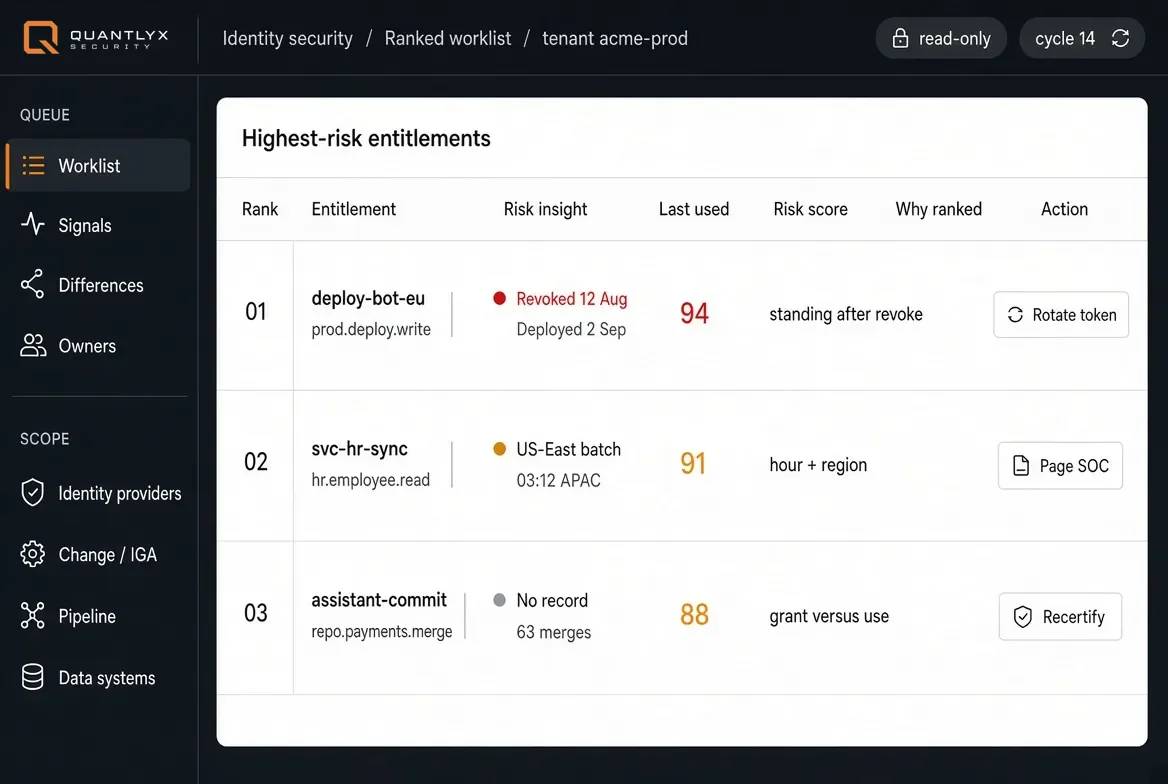
A ranked risk queue with evidence that survives the room.
What a CISO gets from the identity security platform
Entitlement risk, ranked
The entitlements that carry the most risk come first, each with a plain-language definition. No score theatre and no queue of things you already knew.
Non-human identity risk
Service accounts, release bots and coding agents sit on the same register as people. An owner who has gone while the grant stays live is a named finding.
Evidence that survives the room
Each finding traces to the commit, build, deployment or checkout that produced it, with the source record identifier, ready for an auditor or a board.
Read-only, inside your tenant
No agents on hosts and no write path into a pipeline. Nothing leaves your tenant unless you approve a QuantQFix action.
A pilot with a clean exit
A two-week read-only pilot against one lifecycle path. If nothing turns up, you keep a clean report.
An honest coverage map
Quantlyx publishes what it covers and what it does not, including the gaps against the 2026 Top Ten for Agentic Applications.
The thirty-minute demo for this role
The session runs against sample data and stays on the lines that matter to the person in the room.
Risk you can take upstairs
- 0–8Why grant and use disagree, and why that is the perimeter now.
- 8–20Open the ranked worklist on one path. Five lines, owners, actions.
- 20–30Pilot terms: read-only, in tenant, what leaves the room.
Identity is the perimeter. Entitlements are the gaps.
ID entitlement. Rank by risk. Remediate.
Start with a two-week, read-only pilot against one lifecycle path. If nothing turns up, you keep a clean report.