Home / Identity security posture management
Identity security posture management
This identity security posture management (ISPM) is grant versus use, not another inventory. It is not SSPM, which scores SaaS configuration, and it is not CIEM, which looks at cloud entitlements only. Quantlyx scores whether the access an identity holds is being used the way it was approved, for people, service accounts, bots and AI agents.
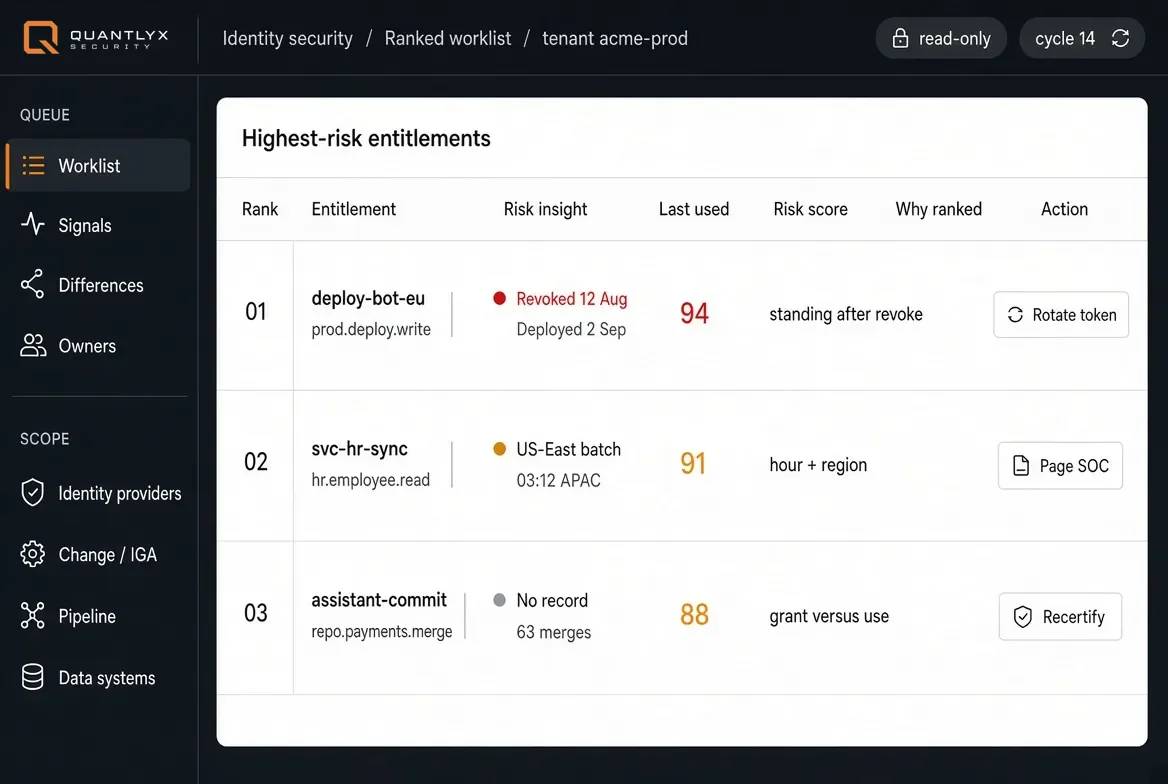
Posture as grant versus use, ranked by risk.
What posture means here
Grant versus use
Each grant is compared with later use. A posture score that never looks at use is an inventory with a number on it.
Ranked by risk
Entitlements are ranked by risk, each with a plain-language definition, so the highest-risk lines come first.
Human and non-human
People, service accounts, build identities, release bots and coding agents sit on one register. See non-human identity security.
What it reads, and what it leaves alone
Quantlyx runs inside your environment with read-only credentials to source control, continuous integration, the artefact registry, deployment, access governance, the privileged access platform and secret stores. It does not read or store your source code, it holds no entitlements and it grants no access.
Findings are routed to the accountable owner with the evidence attached. The threat library scores them as SOC-ready signals for the SIEM, the service desk and change management. See the NHI misuse threat library.
See NHI misuse on your tenant
Read-only pilot. One lifecycle path. If nothing turns up, you keep a clean report.