Home / Products / Just-in-Time access
Just-in-Time access
Standing privilege is the exception. Access is requested, approved, time-boxed and revoked. Multi-approval where the asset requires it. Granular to the resource, the command or the query. Humans, machines and AI agents on the same request path.
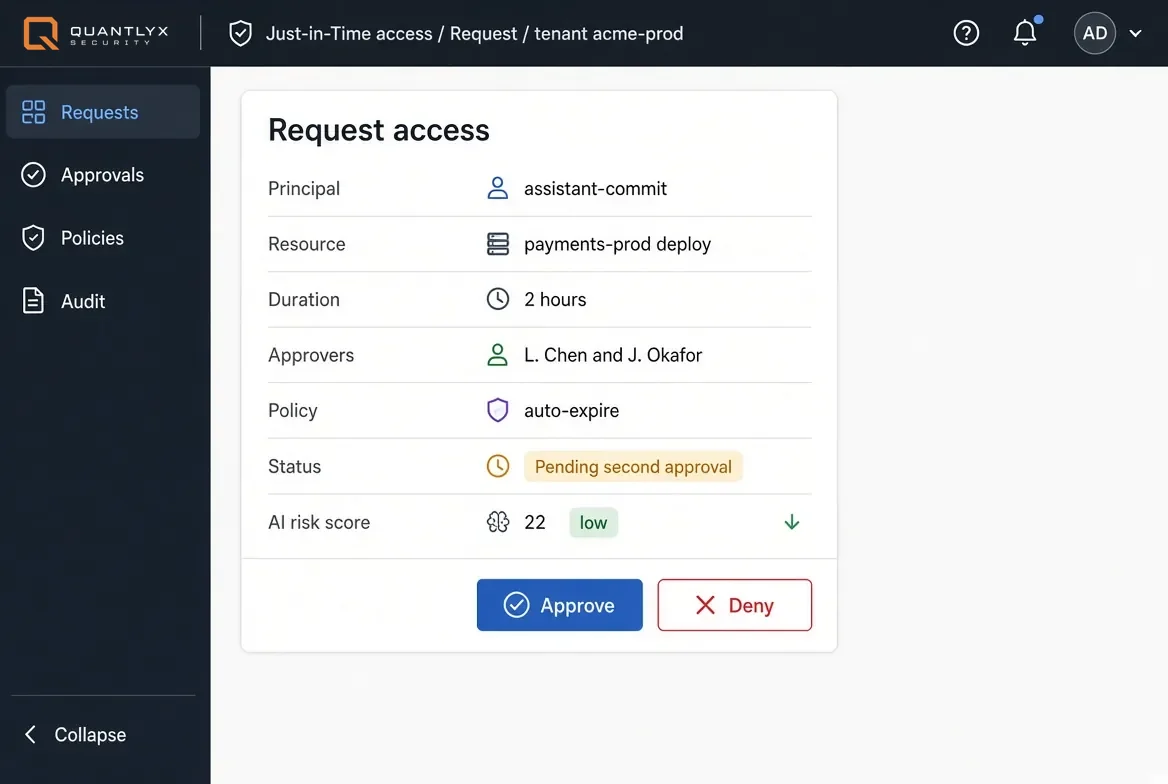
Request · dual approval · auto-expire · risk on the ticket. Access dies when the window dies.
Capabilities
No standing privilege by default
Grant only when needed. Automatic expiration and revocation. The standing token is the finding, not the design.
Granular, individual control
Exact resource, exact duration. Self-service request. Policy decides whether one approver or two.
Multi-approval workflows
Manager and security on the same ticket. Risk score on the request before anyone signs.
Misconfiguration removed at the source
Always-on admin rights are how incidents start. Just-in-Time makes that configuration illegal by default.
AI on the session, not only on the ticket
If the approved window is used off purpose, the session can be terminated. Not a timer with no supervision.
Audit that survives the room
Who asked, who approved, what was used, when it died. Evidence pack, not a log export.
Detect the standing grant. Control the session. Expire the access.
Just-in-Time access removes the standing privilege that the NHI misuse threat library would otherwise have to flag later. It also shrinks the work left for identity threat remediation.
ID entitlement. Rank by risk. Remediate.
Start with a two-week, read-only pilot against one lifecycle path. If nothing turns up, you keep a clean report.